ISC Stormcast For Wednesday, September 16th, 2026 https://isc.sans.edu/podcastdetail/10096, (Wed, Sep 16th)
No summary available.
No summary available.
The fabricated footage parodied a post-game interaction following Texas’ 24-23 comeback victory over Ohio State on Saturday
A likely North Korean advanced persistent threat (APT) group used a previously undocumented Linux espionage toolkit to compromise load balancers, gain access to communications, and further exploit networks.
Acronis disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WebHost Manager (WHM), and Plesk that may be exploited in the wild. [...]

You can't make an omelet without breaking a few eggs, and you can't patch nearly 1,000 CVEs without a few glitches.
Microsoft agreed to adopt guardrails and privacy standards for its AI in schools, as negotiated with the American Federation of Teachers. The post Microsoft Commits to Sweeping AI Privacy Rules for Students. Will Other Tech Giants Follow? appeared first on SecurityWeek.

Malicious versions of the Admin Menu Editor Pro plugin for WordPress have been distributed to more than 200 customers after a threat actor compromised the maintainer's website and pushed updates that created a hidden user account. [...]

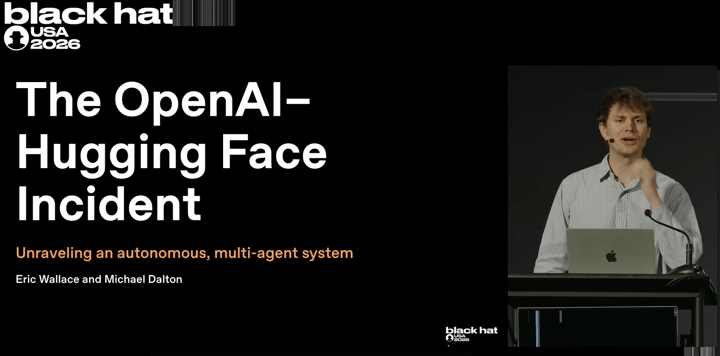
The 'Breaking' News: The OpenAI–Hugging Face Incident - A Technical Reconstruction and Its Implications for AI At this Black Hat USA 2026 talk, OpenAI security engineers and researchers will reconstruct the OpenAI-Hugging Face incident and examine its implications for AI security, cyber resilience, and align…
Point-in-time audits and sampled assessments offer only snapshots; continuous control monitoring provides evidence that security controls are working today. The post “We Think the Security Control Is Working” Is No Longer Good Enough appeared first on SecurityWeek.
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat actor has used lures that impersonate a dozen…

Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran's intelligence service uses to spy on dissidents, journalists, and activists around the world. The malware is controlled via the Telegram messaging app and can copy a target…

The full-service malware-as-a-service (MaaS) platform offers a Windows implant, command-and-control (C2) infrastructure, and an operator panel for comprehensive remote access.
It was discovered that kitty incorrectly escaped error messages when handling specially crafted terminal escape sequences. A remote attacker could possibly use this issue to execute arbitrary commands. (CVE-2026-42850) It was discovered that kitty incorrectly handled remote edit requests in terminal output.…
It was discovered that SRT did not authenticate certain encryption control messages. A remote attacker could possibly use this issue to downgrade an encrypted connection and inject arbitrary content or interrupt a media stream. (CVE-2026-55868) It was discovered that SRT did not properly validate certain con…
Cédric Krier discovered that python-sql incorrectly escaped values passed to unary operators. An attacker could possibly use this issue to perform SQL injection attacks.
Guillem Lefait discovered that Suricata-Update did not properly validate destination paths when extracting files referenced by downloaded rule archives. An attacker could possibly use this issue to write arbitrary files outside the configured rules directory.
It was discovered that Snapcast incorrectly handled crafted JSON-RPC requests. A remote attacker could possibly use this issue to execute arbitrary code or obtain sensitive information.
Florian Stuhlmann discovered that Shibboleth incorrectly escaped input when using the ODBC storage plugin. A remote attacker could possibly use this issue to perform SQL injection attacks and obtain sensitive information.
It was discovered that phpseclib did not perform padding validation in constant time when using AES in CBC mode. A remote attacker could possibly use this issue to conduct a padding oracle timing attack and obtain sensitive information.
It was discovered that SimpleSAMLphp incorrectly validated cryptographic signatures in XML messages. An authenticated attacker could possibly use this issue to impersonate users or gain elevated privileges. This issue only affected Ubuntu 16.04 LTS and Ubuntu 18.04 LTS. (CVE-2019-3465) It was discovered that…
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to access live video and sensitive device information, enable unauthorized services, execute arbitrary code, modify device operation, and recover stored credentials. The following versions of CareCam CM2507 are affecte…
View CSAF Summary Siemens Reyrolle 7SR5 Before V2.70 is affected by multiple vulnerabilities. Siemens has released a new version for Reyrolle 7SR5 and recommends to update to the latest version. The following versions of Siemens Reyrolle 7SR5 are affected: Reyrolle 7SR5 vers:intdot/<2.70 (CVE-2024-42384, CVE…
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to deliver an unauthorized update, execute code, or extract credentials to allow the attacker to impersonate a privileged client. The following versions of Wärtsilä FOS-Onboard are affected: FOS-Onboard 5.07.0923.01 (C…
View CSAF Summary Mendix SAML module contains a vulnerability that could allow unauthenticated remote attackers to hijack an account in specific SSO configurations. Mendix has provided fix releases for the Mendix SAML module and recommends to update to the latest version. The following versions of Siemens Me…
View CSAF Summary A reflected cross site scripting vulnerability in the authentication redirect flow (/auth/) of Teamcenter allows an unauthenticated remote attacker to inject JavaScript into an authenticated user's session by crafting a malicious URL. Successful exploitation may enable the attacker to read…